Security scans that tell you exactly what to fix.
secscan runs nuclei, semgrep, trivy, gitleaks, OWASP ZAP, and more against your apps and repos. Each finding comes back with a paste-ready fix, not generic advice. Free open-source CLI today. Hosted weekly scans coming soon.
Why secscan
The same scanners you'd run yourself, glued together, with the boring parts done for you.
One CLI, twelve scanners
Headers, TLS, subdomain enumeration, port scan, nuclei templates, ZAP, ffuf, semgrep, trivy, gitleaks. Risk-gated so you can't accidentally fire an aggressive scan at production.
Continuous, not one-off
Hosted version runs your scan on a schedule, diffs against the previous run, and emails you only what's new. No more re-triaging the same findings every week.
Fixes you can paste
Every finding gets a curated remediation block. With an Anthropic API key, Claude reads your _headers or code snippet and tells you the exact line to add.
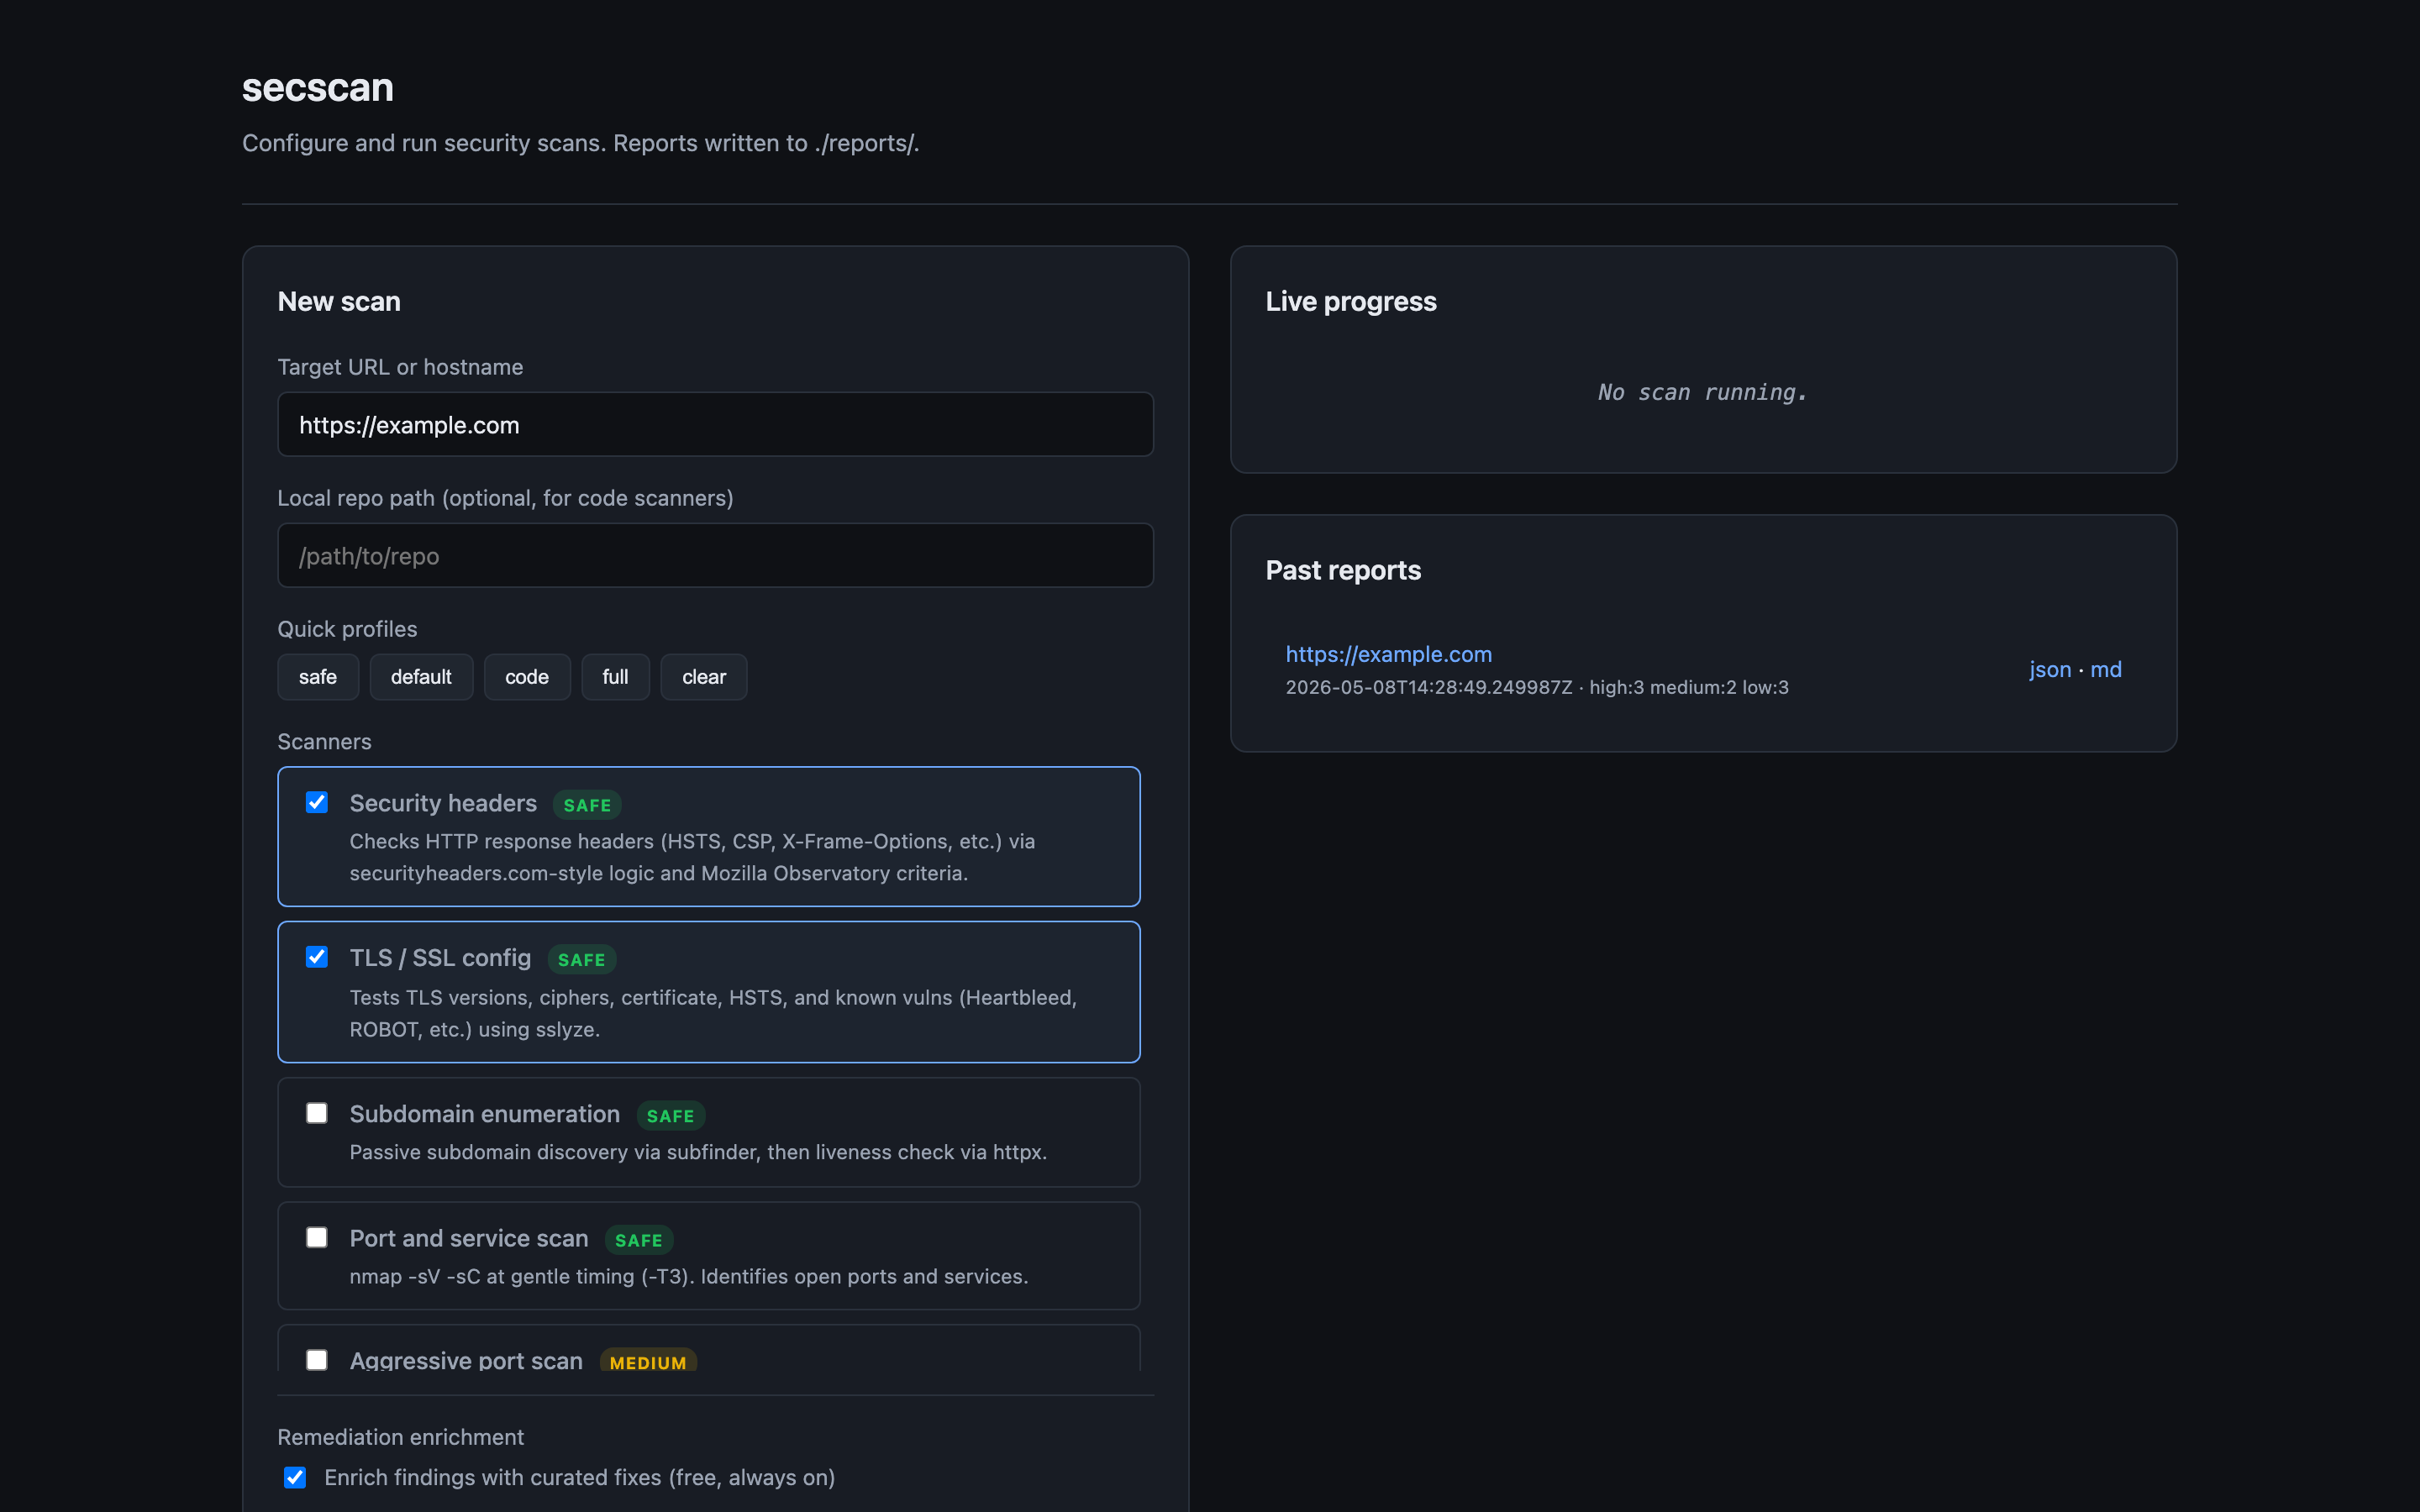
What it looks like
Same dashboard whether you self-host or use the hosted version.
Pricing
Self-host the CLI free forever. The hosted version is what we're building next.
Self-host
$0 / free, MIT
- Full CLI and dashboard
- All scanners
- Bring your own Anthropic key
- Run anywhere you can run Docker
Hosted Solo
~$9 / month
- Up to 3 targets
- Daily scans
- AI-tailored fixes
- Email alerts on new findings
- 90 days of history
Hosted Team
~$99 / month
- Up to 15 targets
- Hourly scans
- Slack and webhook alerts
- 1 year of history
- Multi-seat (when available)